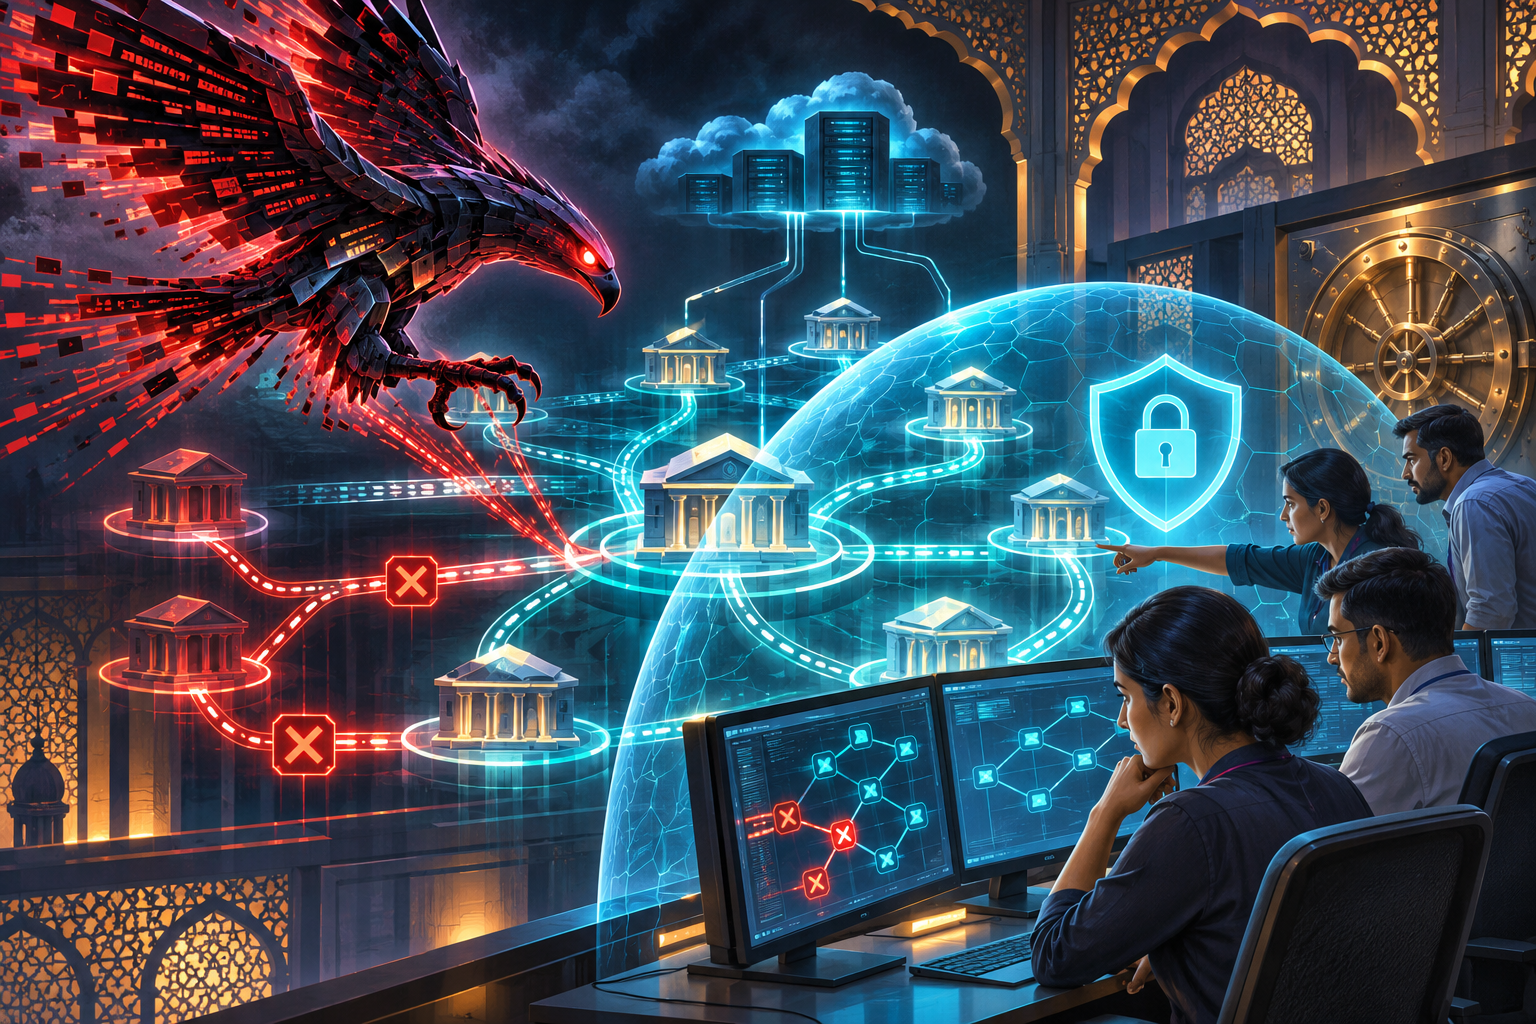
NEW DELHI - India's national cybersecurity agency has warned banks and other financial businesses about an active campaign in which attackers use publicly available artificial-intelligence tools to probe systems, exploit weaknesses and move money at what the agency called machine speed.
The Indian Computer Emergency Response Team, known as CERT-In, issued a critical advisory on Wednesday naming the threat actor Crafty Falcon. The campaign has targeted non-bank lenders, digital lending platforms, financial-technology companies, payment providers and cryptocurrency exchanges, according to the agency and reporting on the advisory.
CERT-In said the attackers survey targets with machine intelligence and automate complete attack chains. The systems can generate large numbers of tailored scripts, adapt their behavior to a target's response and rotate internet infrastructure quickly, reducing the time defenders have to detect and stop an intrusion.
The agency identified four offensive tools used in the campaign: ARTEX, PentAGI, Cairn and CyberStrikeAI. These systems were built for penetration testing or security research and are available publicly, illustrating how software designed to help defenders can also be repurposed for theft.
At least two of the tools have separate links to China, according to security researchers. ARTEX was developed in China, and CrowdStrike said an unidentified attacker likely to be a Chinese speaker used the framework against South Korean financial organizations from late September into early October. CrowdStrike assessed the attacker as financially motivated and did not attribute the activity to the Chinese government.
CERT-In also did not identify who operates Crafty Falcon, where the group is based or whether any state sponsors it. Its advisory did not say that Beijing directed the Indian campaign. The distinction is important: a Chinese-developed tool and Chinese-language activity can support an investigative lead, but they do not by themselves prove government responsibility.
The attackers appear to focus on the interfaces that connect financial institutions. CERT-In said Crafty Falcon targets payment and disbursement systems, exposed application programming interfaces, cloud-management services and internet-facing test environments. Compromised APIs can allow criminals to send instructions through a victim's own trusted channels.
Attacks have been timed for holidays, weekends and other periods with lighter monitoring. The agency said some firms were targeted again after making incomplete repairs following earlier warnings. It urged around-the-clock monitoring, tighter separation between testing and production systems, stronger cloud and API controls and automated detection of unusual transactions.
Recent incidents show why the warning is urgent, although CERT-In did not say which were connected to Crafty Falcon. Two Mumbai non-bank lenders lost about $2 million through more than 700 unauthorized instant transfers in October, according to Reuters. Spandana Sphoorty Financial separately disclosed unauthorized debits totaling 78 million rupees from one of its accounts on November 1, while AU Small Finance Bank has investigated a possible customer-data leak.
The advantage is moving toward the fastest attacker
Cybersecurity has always been an unequal contest. A defender must protect every important doorway; an attacker needs to find one opening. AI automation makes that imbalance worse because it can test weaknesses continuously, rewrite code after a failed attempt and coordinate steps that previously required a larger team.
The danger is not that an autonomous system has replaced every human hacker. The more immediate threat is that one operator can now work with the speed and persistence of many. Low-cost tools can turn known vulnerabilities, exposed credentials and weak test servers into a production line for intrusion.
Financial institutions are particularly vulnerable to this change because they are connected by design. Banks, fintech platforms, payment processors, cloud providers and lending partners exchange instructions through APIs. That connectivity makes modern finance efficient, but it also means a weakness at a smaller company can reach a larger institution's payment rails.
China's role requires disciplined scrutiny rather than careless accusation. Open-source tools cross borders, and criminals can use Chinese software without taking orders from the Chinese Communist Party. At the same time, democratic countries would be reckless to ignore repeated cases in which China-based or China-aligned actors use advanced cyber capabilities against foreign institutions.
The correct response is evidence-led attribution, shared intelligence and stronger defenses. India, the United States, South Korea and other democracies should exchange technical indicators rapidly, pressure technology platforms to remove malicious infrastructure and impose consequences when investigators can establish responsibility.
Companies also need to abandon the idea that cybersecurity is a periodic compliance exercise. A patch that is incomplete, a test environment connected to production or an alert queue left thin over a holiday can become the entry point for a machine-speed attack. Boards should demand proof that critical systems are monitored continuously and that payment anomalies can be stopped before money leaves.
AI will strengthen defenders as well as attackers, but that is not automatic. Criminals can adopt a useful tool immediately; regulated institutions move through budgets, procurement and approval chains. The organizations that shorten that delay without weakening oversight will be the ones most likely to withstand the next campaign.
Comments
Loading comments…